

vulnerability
Blog post
Can’t Patch PHP2Shell Yet? Build a Stopgap with the Controls You Own
Source: Qualys Security Blog · Published · Last checked 3 hours ago · 1 min read
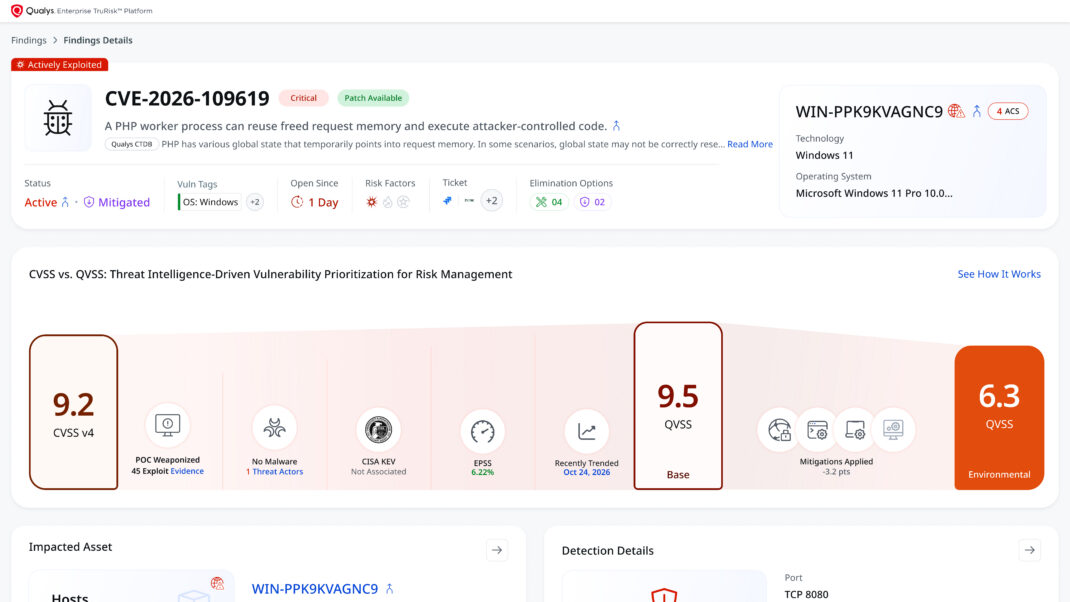
Publisher excerpt From Qualys Security Blog
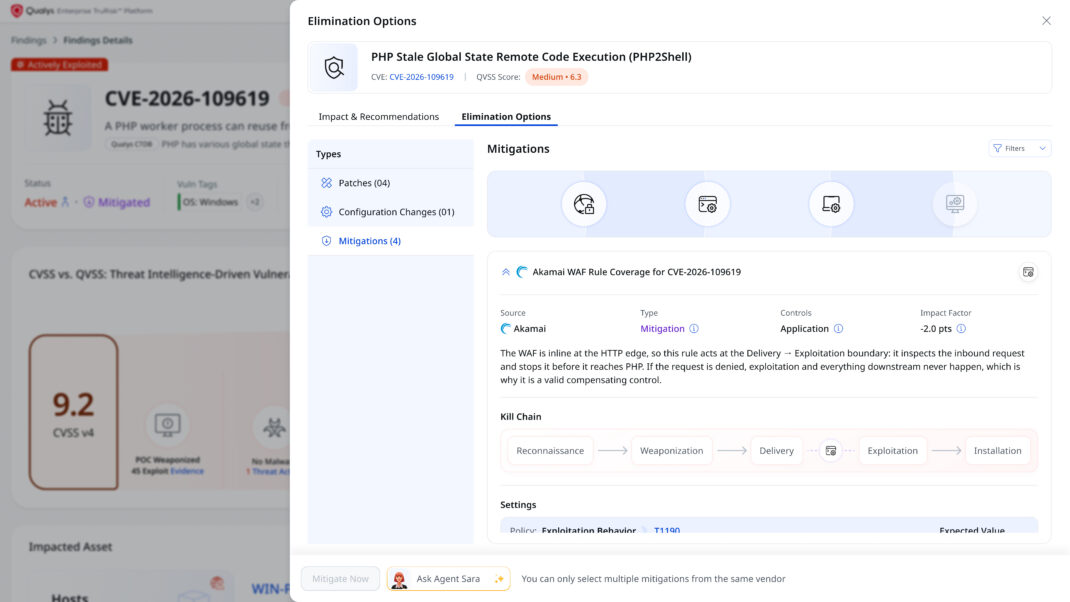
Executive Summary PHP2Shell’s fix is to update PHP, but patching at scale is slow. Only 199,000 of 156 million PHP installations were patched in the first 12 hours after disclosure. In the meantime, Qualys’s configuration-level mitigation reduces exposure to the confirmed attack path without code changes, with or without an agent. WAF, IPS, and EDR […]
Excerpt only, shown with attribution. This content belongs to the original publisher and has not been independently verified by CyberSecurity.pk.
More images
Keywords: vulnerabilityproduct and techphp2shellvulnerabilitiesvulnerability managementvulnerability newsQualys Security Blogcybersecurity newssecurity news Pakistan
Reference: Qualys Security Blog — blog.qualys.com ↗