

vulnerability
Blog post
Node.js Patches Brotli Remote Code Execution Flaw: Find Vulnerable Runtimes Before Attackers Do
Source: Qualys Security Blog · Published · Last checked 3 hours ago · 1 min read
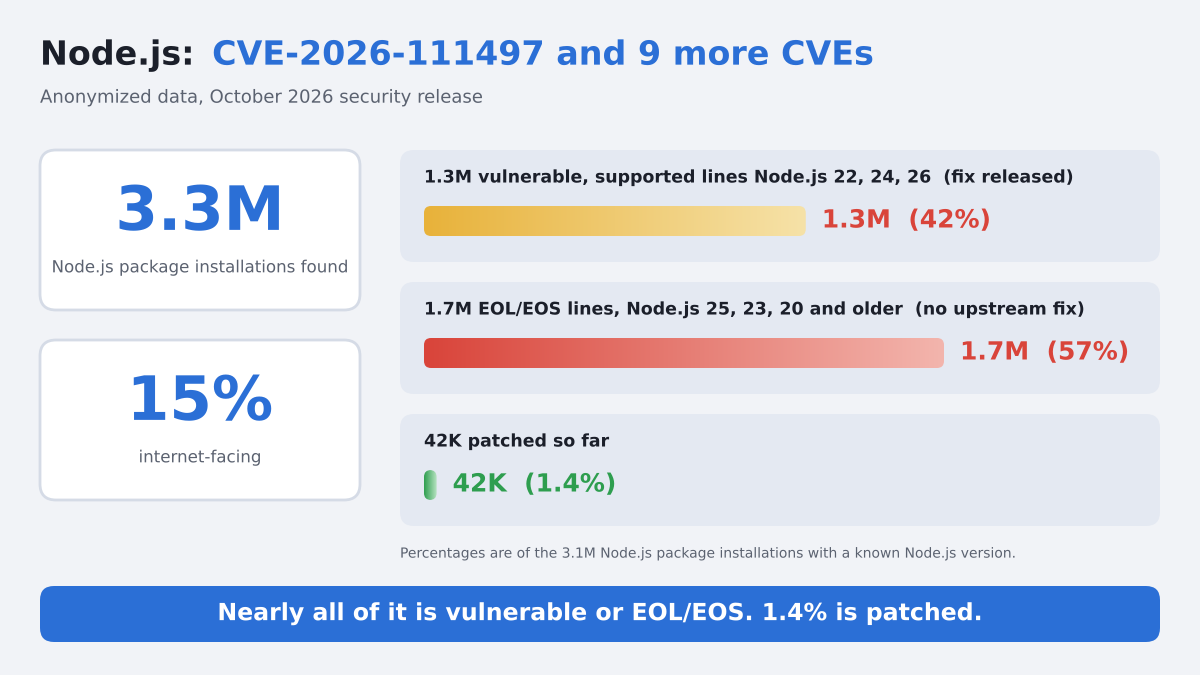
Publisher excerpt From Qualys Security Blog
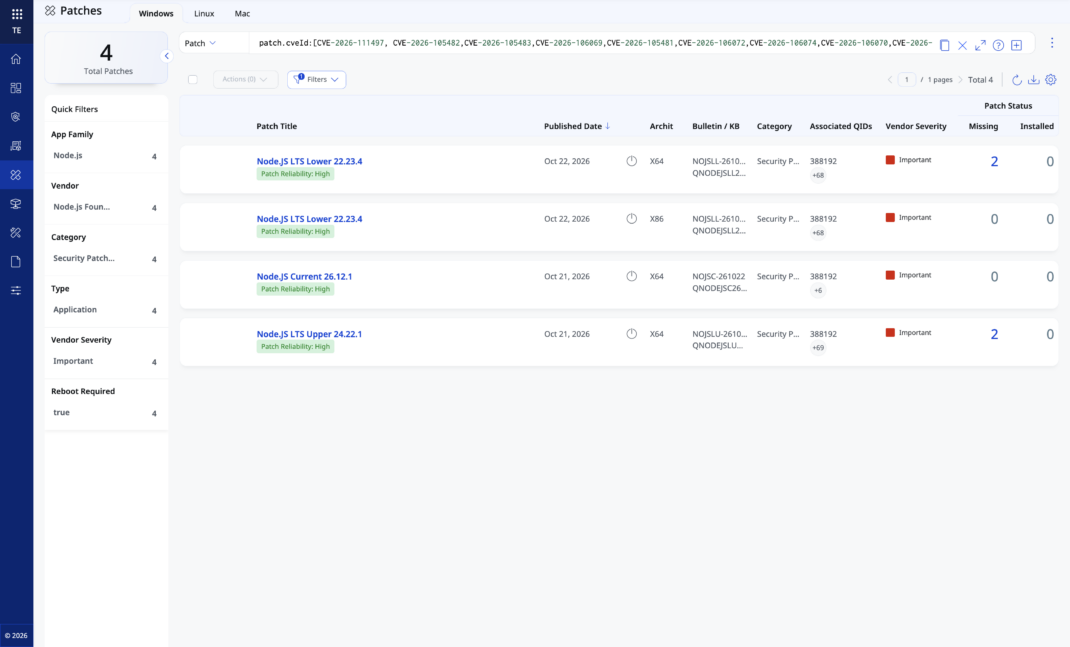
Executive Summary On October 21, 2026, Node.js released fixes for 10 vulnerabilities across its three supported release lines: 22.x, 24.x, and 26.x. Four are rated High. The most severe, CVE-2026-111497, is an out-of-bounds write in the bundled Brotli decoder that Node.js says permits remote code execution. These flaws live in the Node.js runtime itself, not […]
Excerpt only, shown with attribution. This content belongs to the original publisher and has not been independently verified by CyberSecurity.pk.
More images
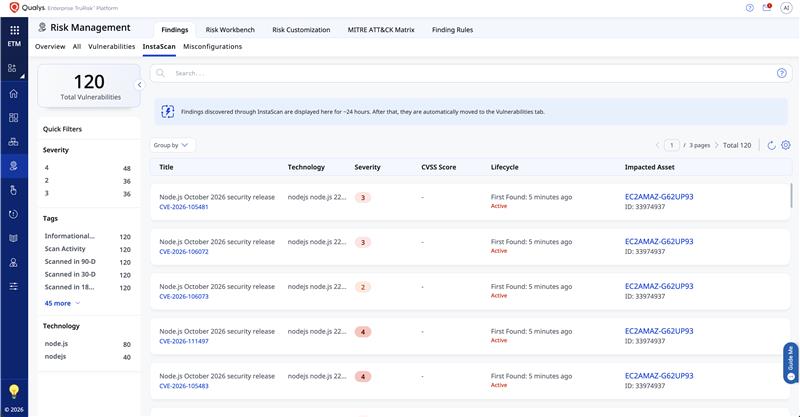
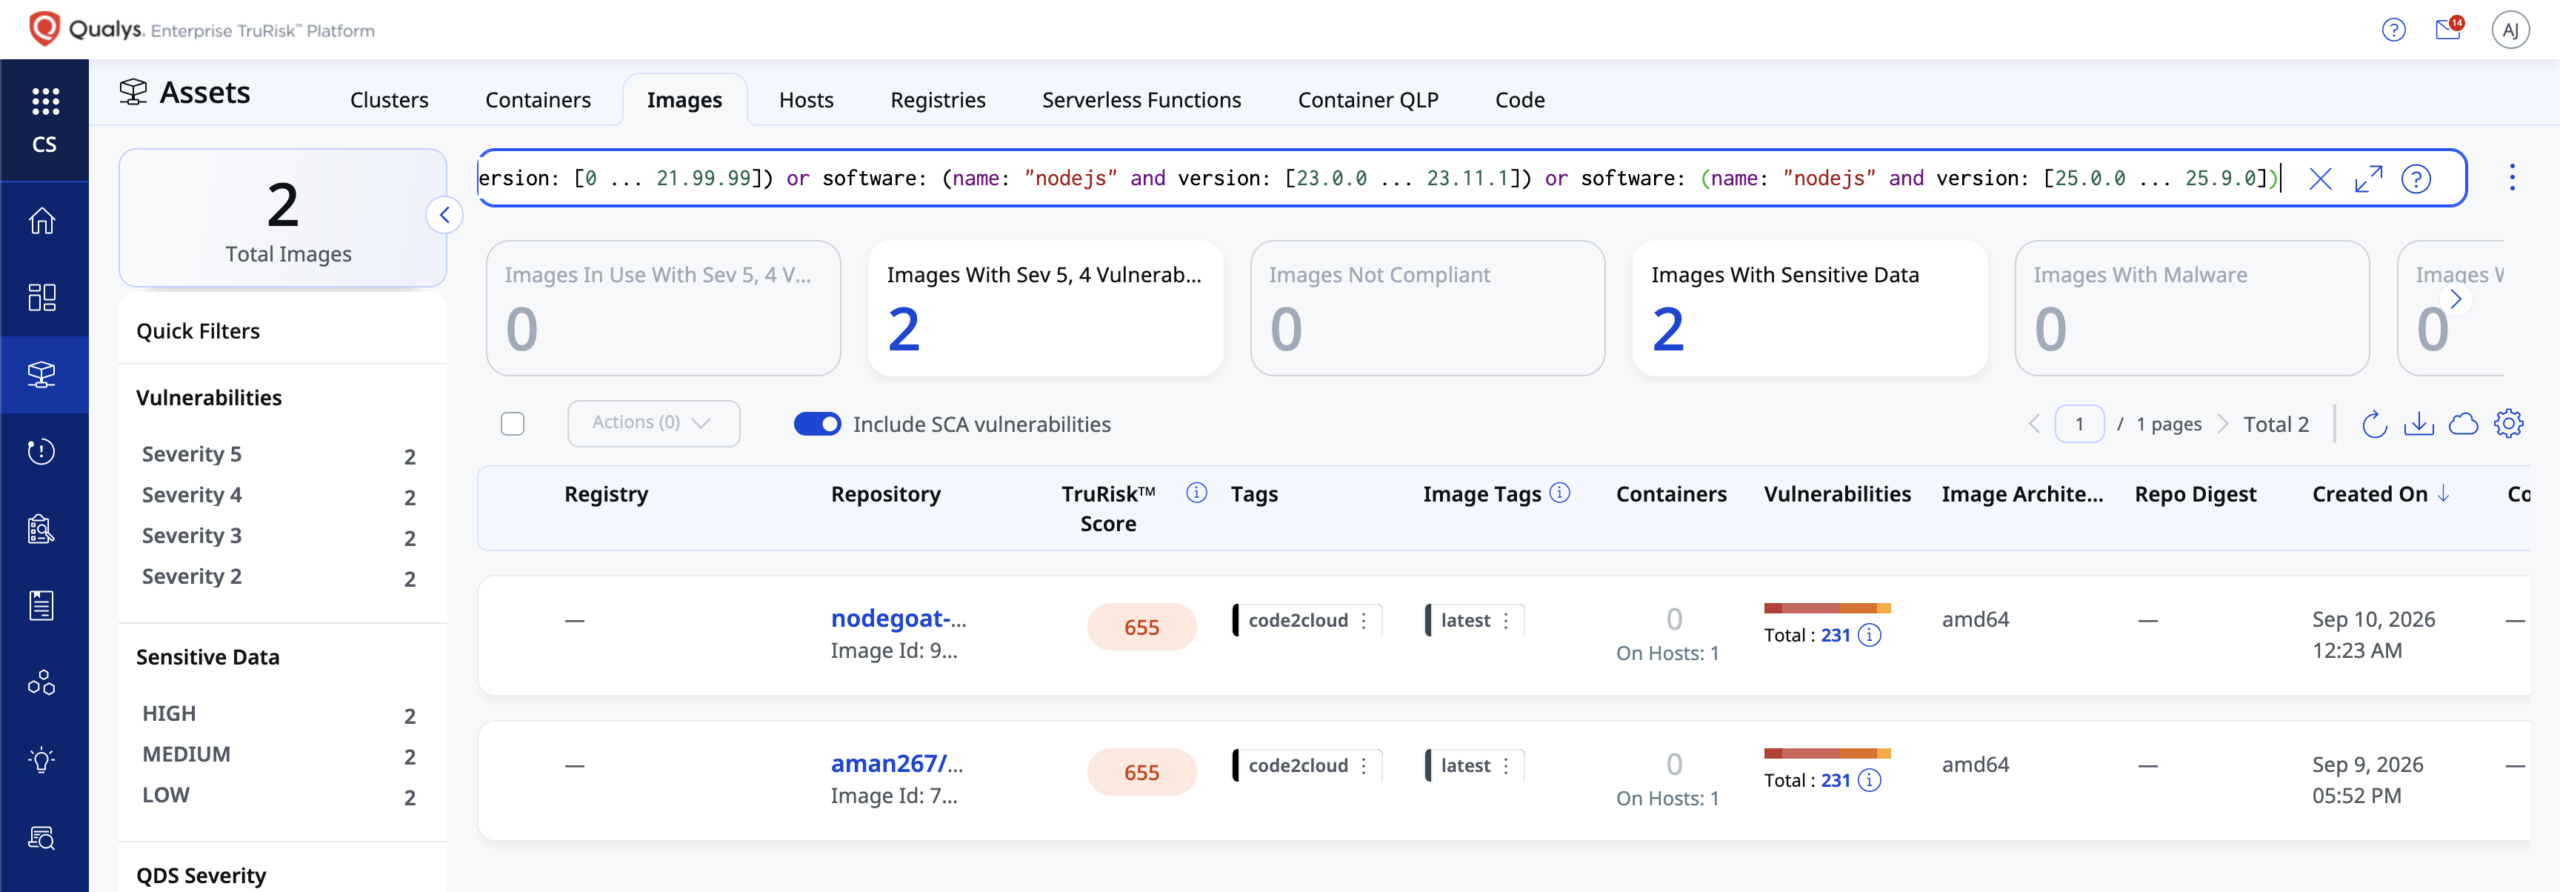
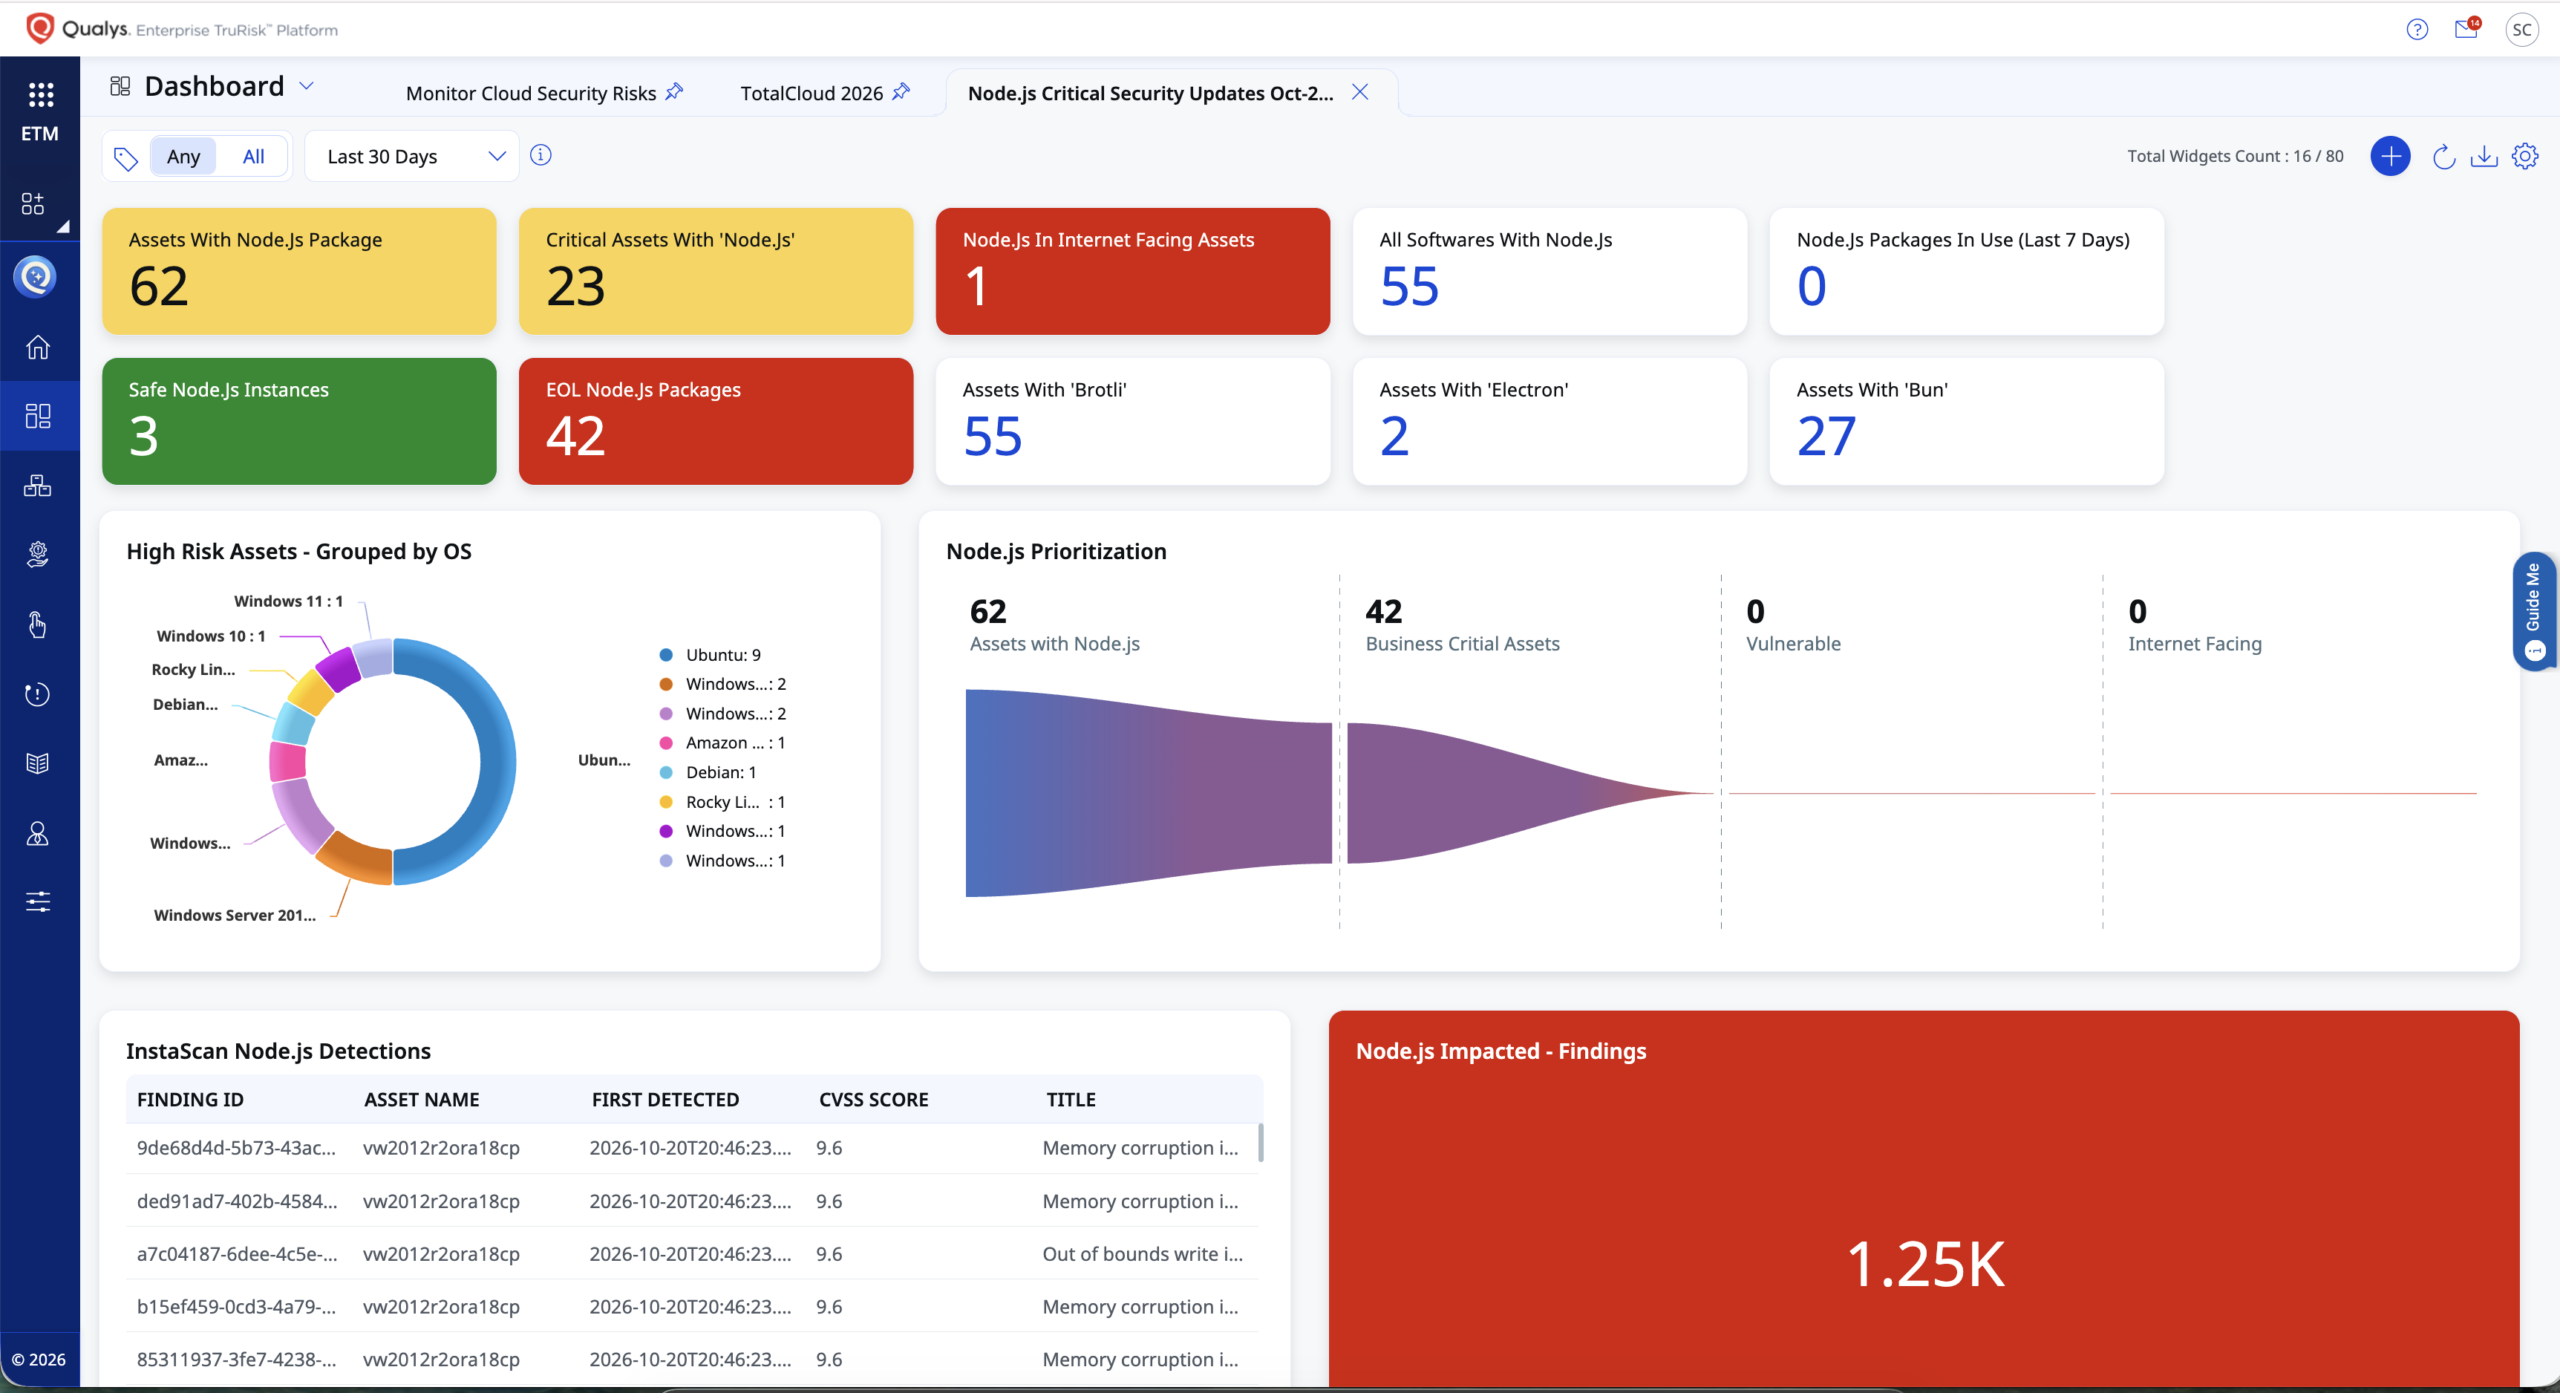
Related CVEs
Keywords: remote code executionawsproduct and techcve-2026-111497nodejsqualys truriskremotecodeexecutionsecurityupdatevulnerabilityvulnerability newsQualys Security Blogcybersecurity newssecurity news Pakistan
Reference: Qualys Security Blog — blog.qualys.com ↗