

vulnerability
Blog post
Two Critical PHP Flaws Could Hand Attackers Your Web Servers. Here’s How to Find, Mitigate, and Patch PHP2Shell Now
Source: Qualys Security Blog · Published · Last checked 3 hours ago · 1 min read
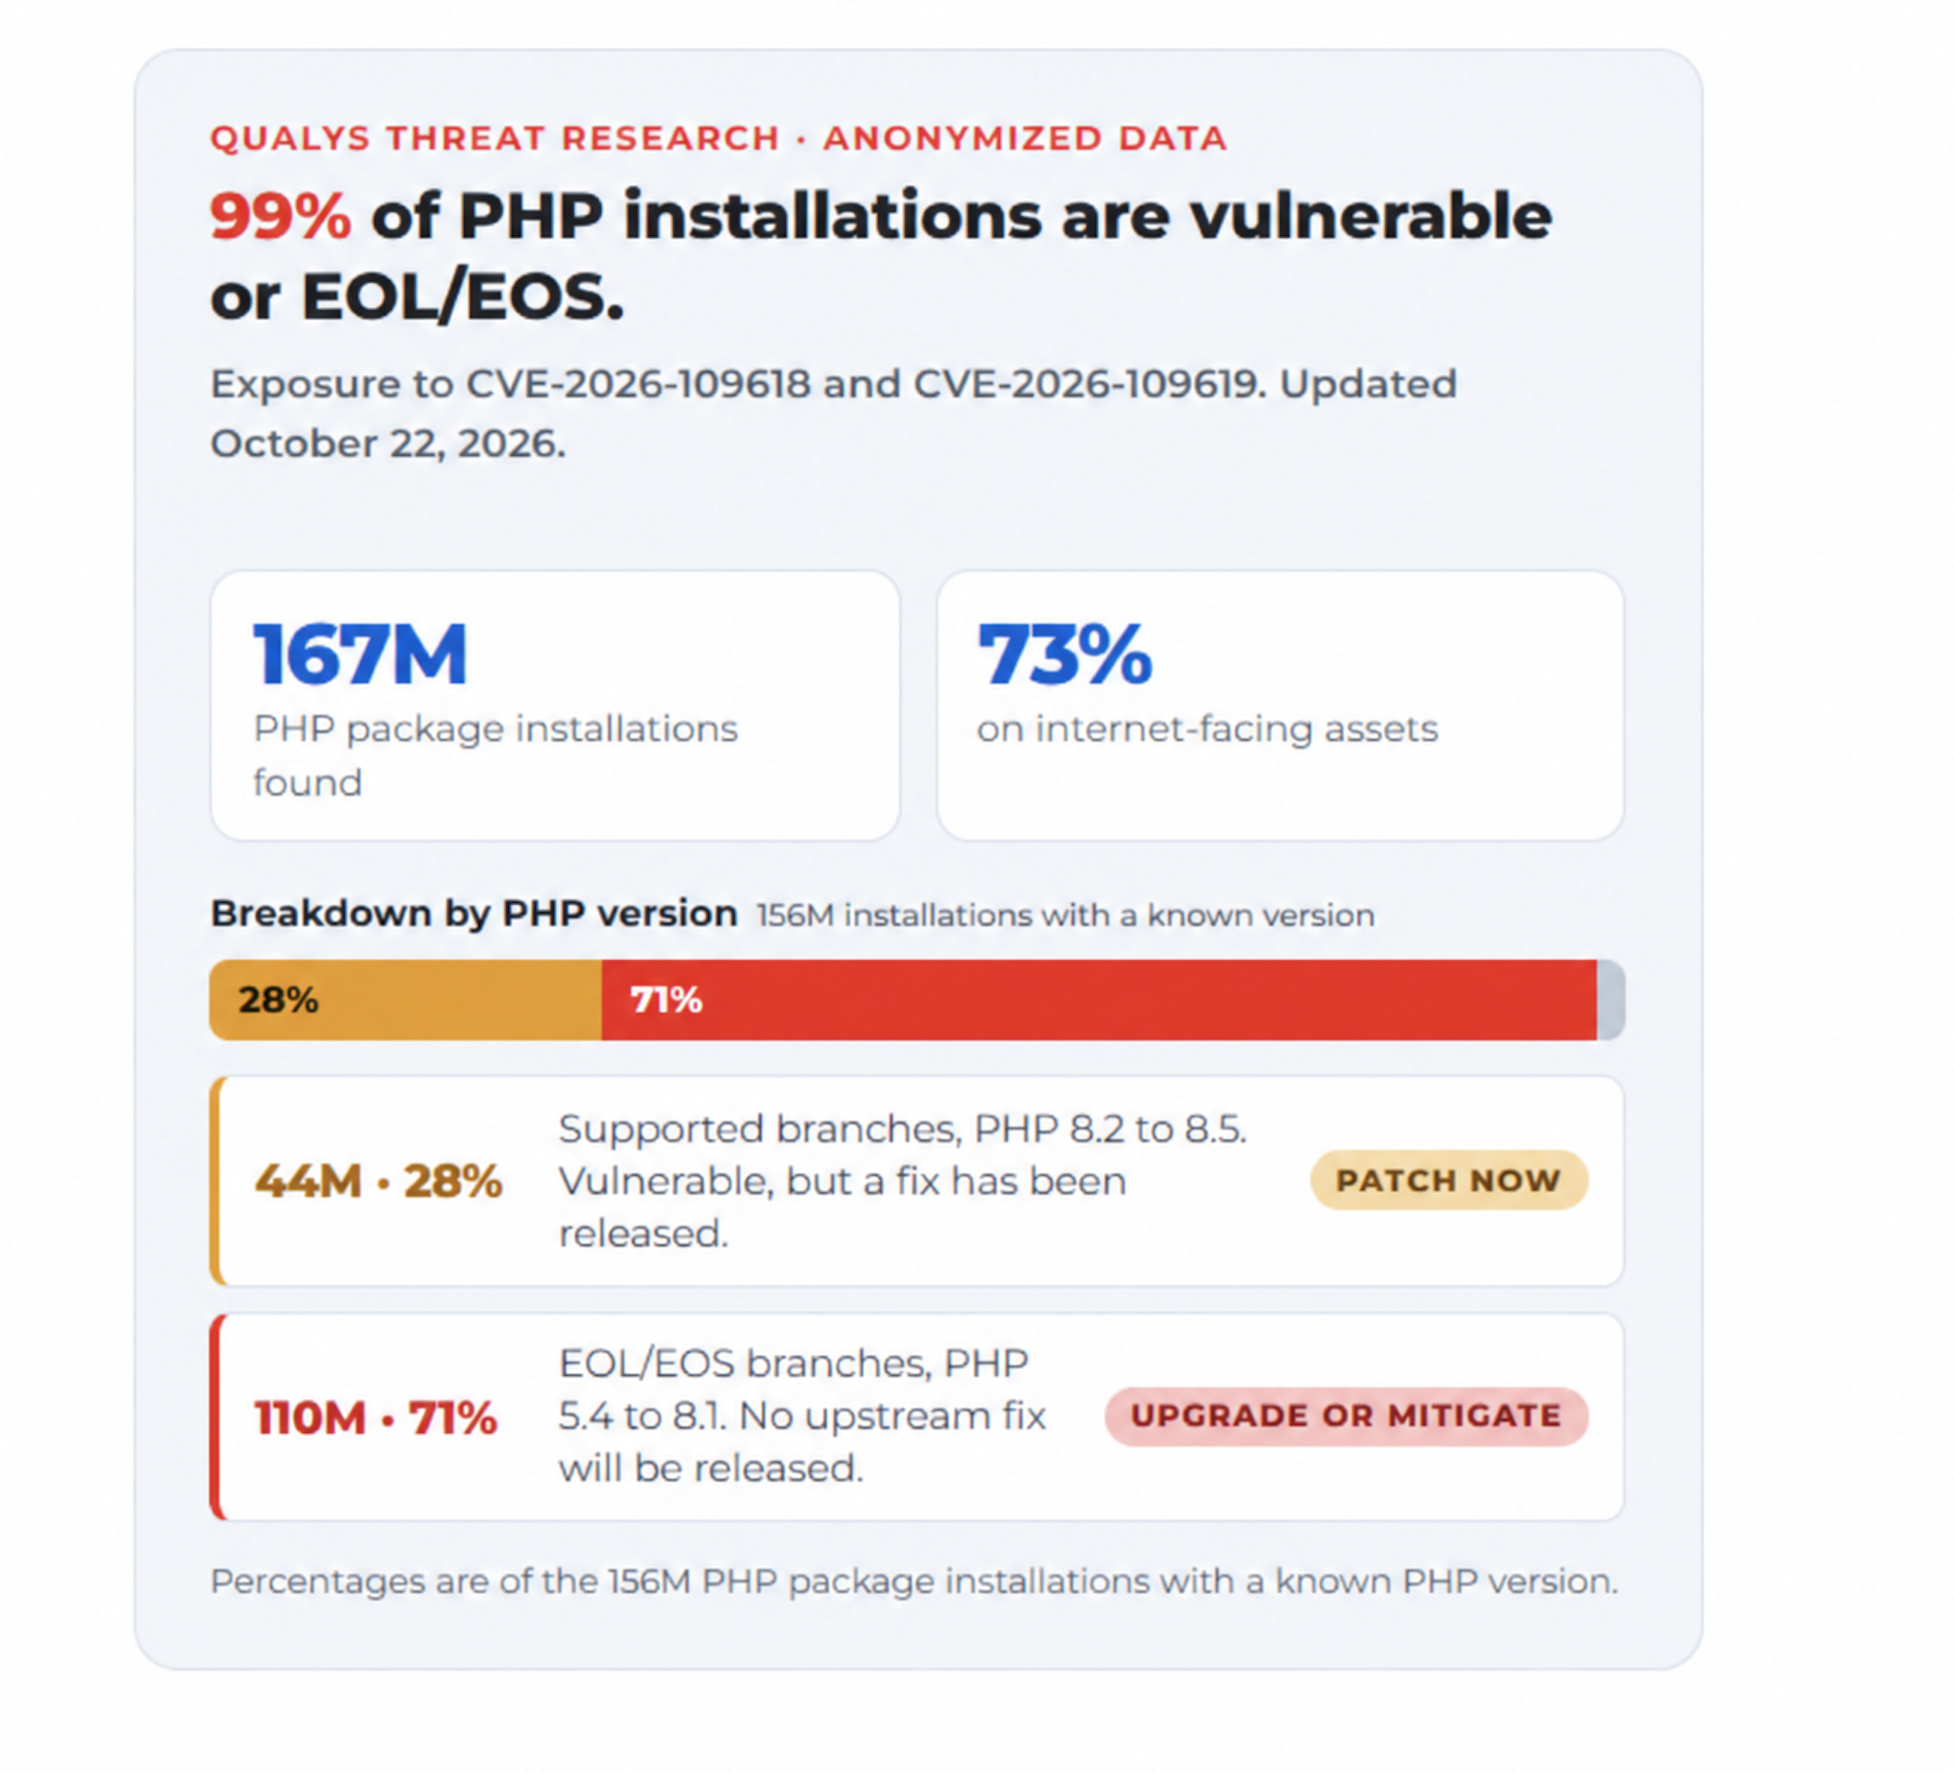
Publisher excerpt From Qualys Security Blog
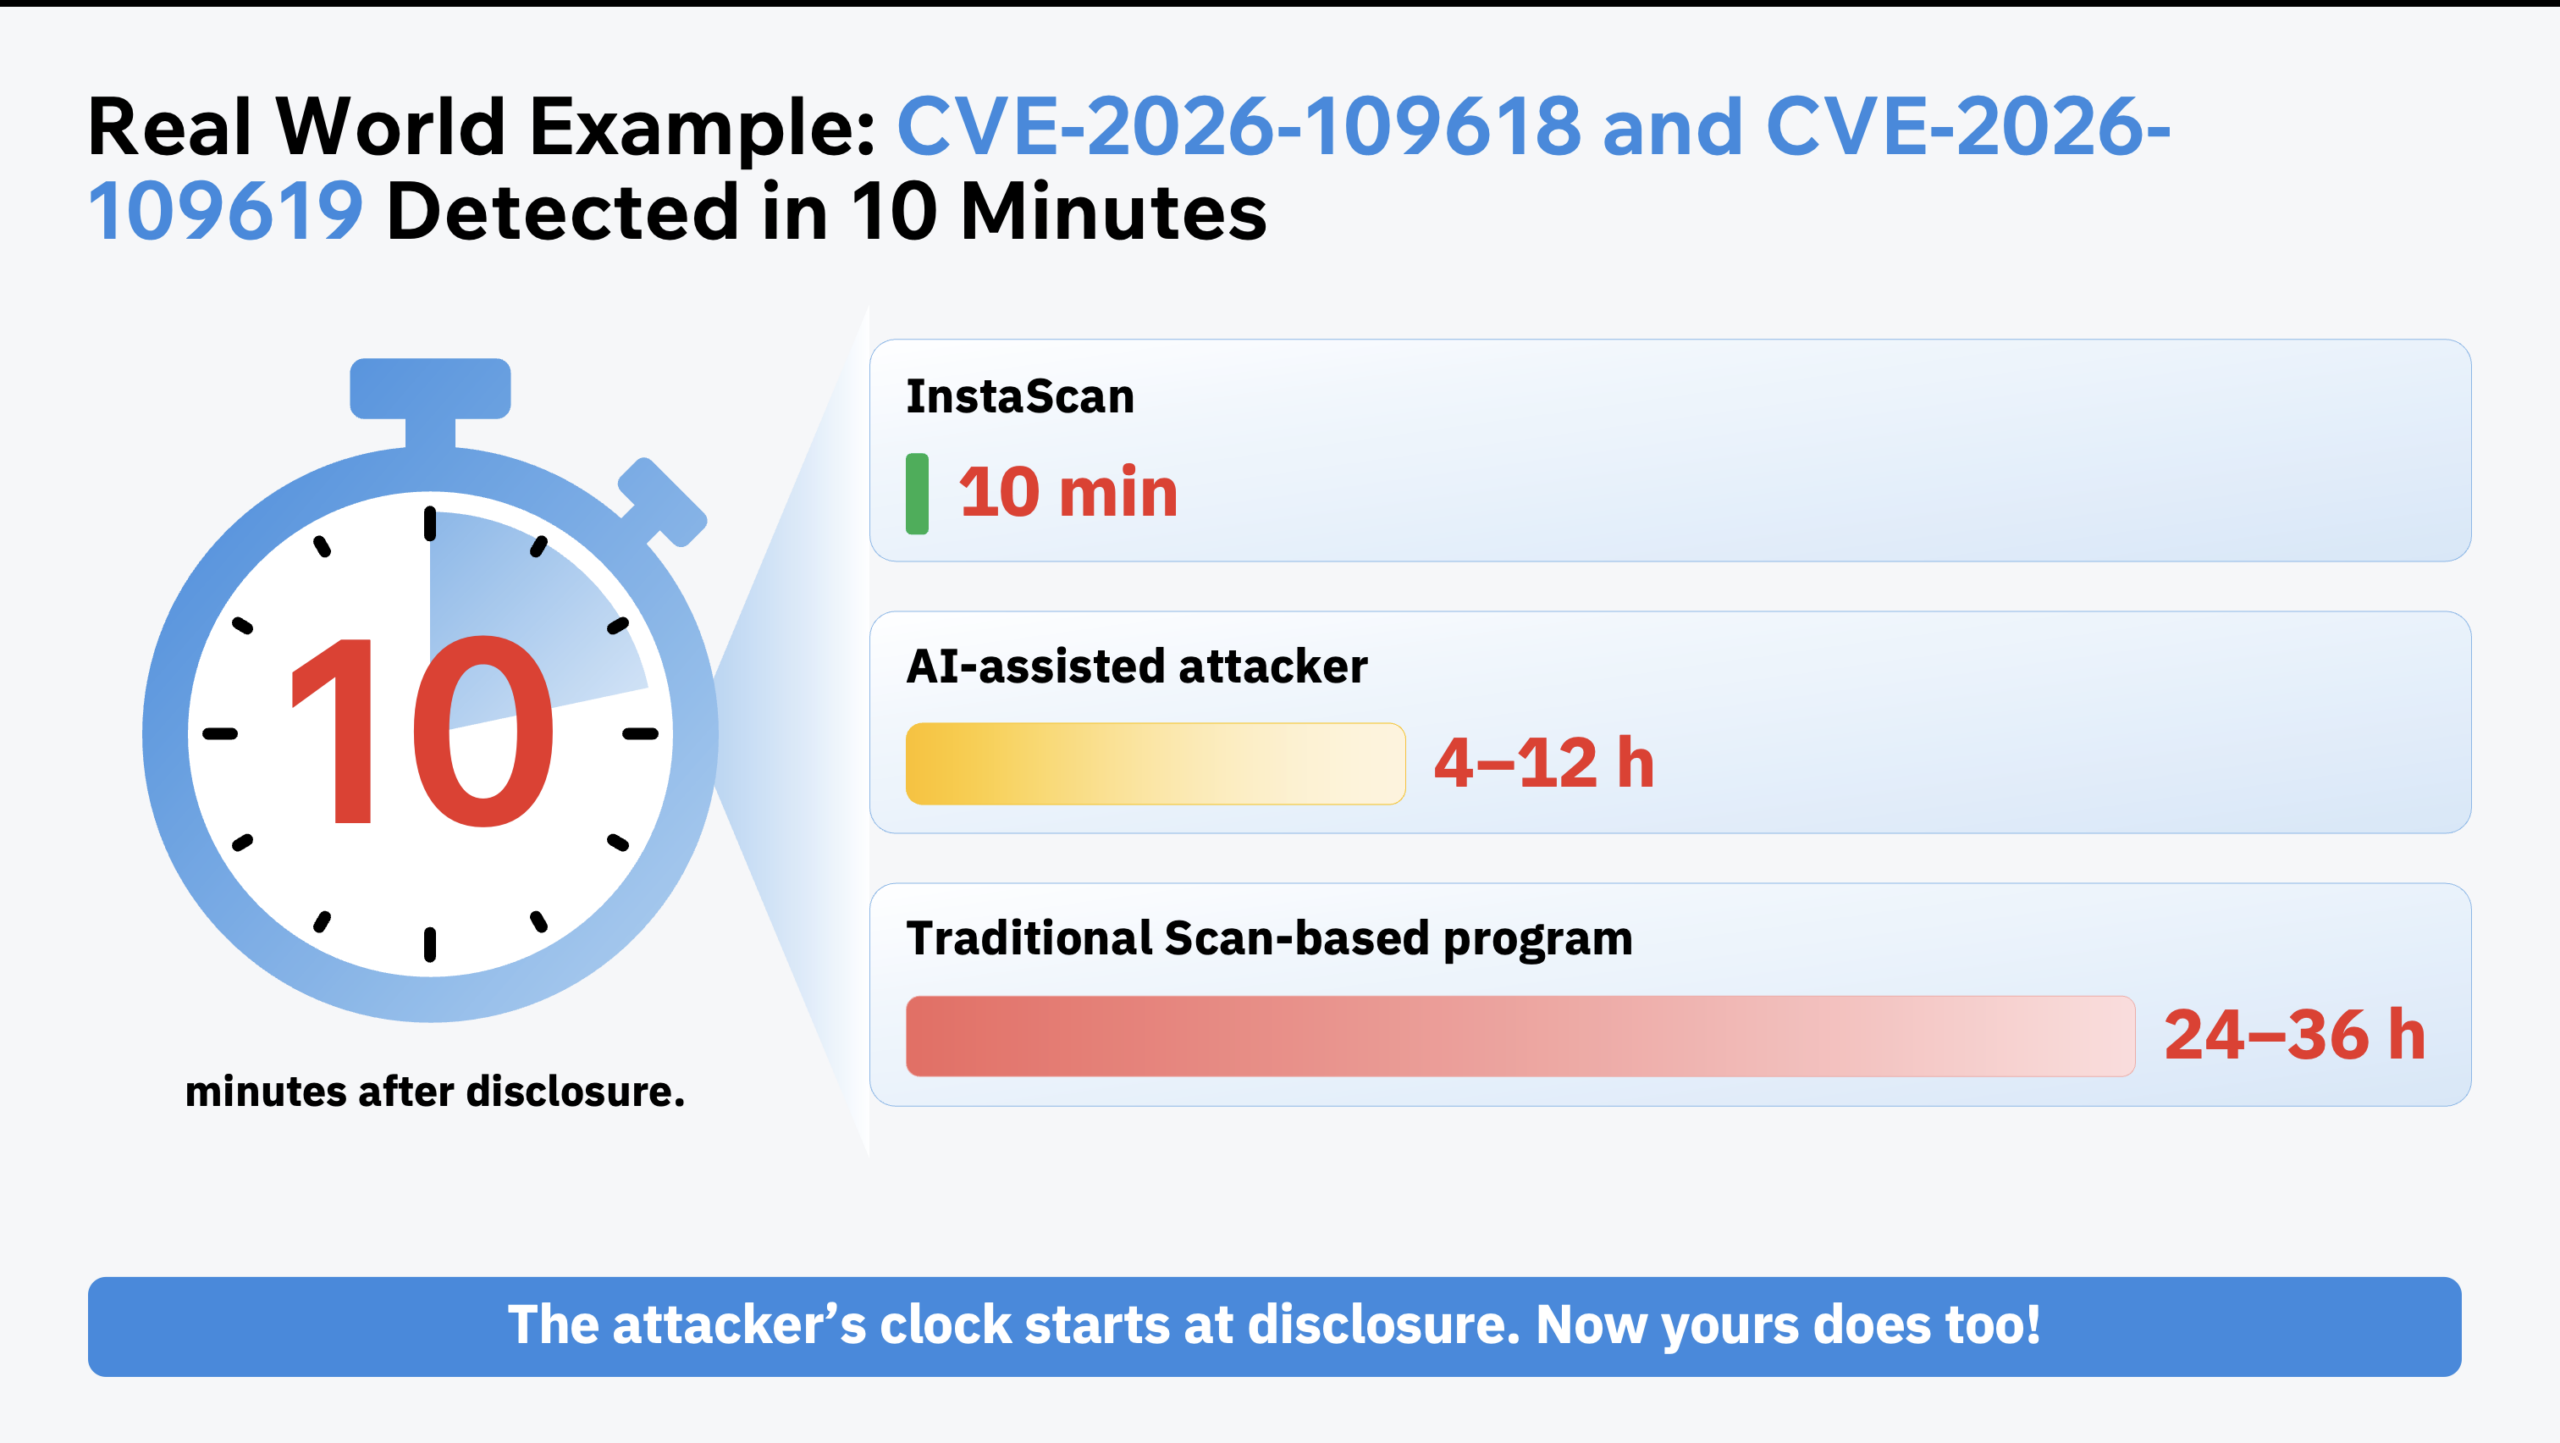
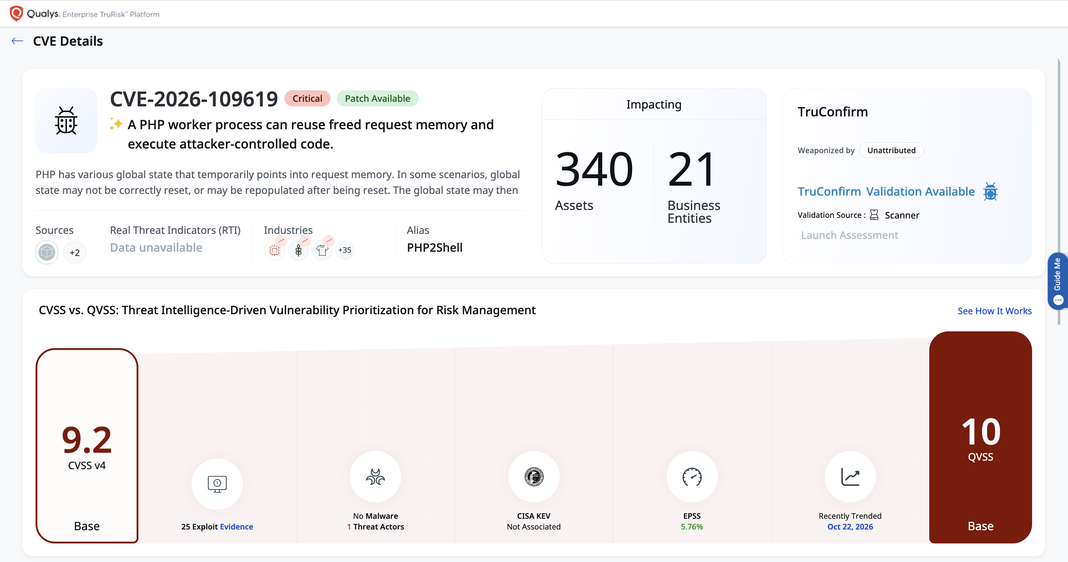
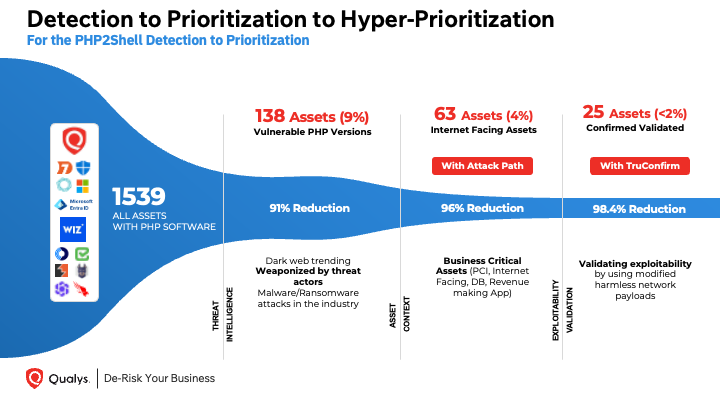
Executive Summary PHP2Shell refers to two critical vulnerabilities (CVE-2026-109618 and CVE-2026-109619), each with a CVSS v4.0 score of 9.2, that can allow unauthenticated remote code execution on PHP installations serving web requests. Researchers have also demonstrated unauthenticated disclosure of PHP worker memory, which can expose passwords, authentication tokens, and API keys. Cloudflare has already reported […]
Excerpt only, shown with attribution. This content belongs to the original publisher and has not been independently verified by CyberSecurity.pk.
More images
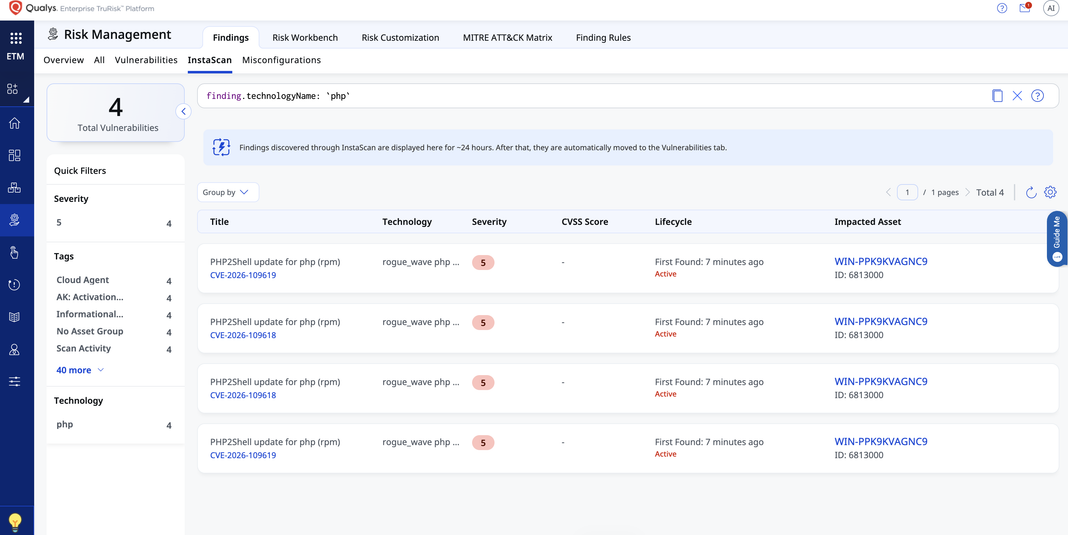
Related CVEs
Keywords: rceremote code executionawsphpthreatsvulnerabilitiesCVE-2026-109618CVE-2026-109619vulnerabilityvulnerability newsQualys Security Blogcybersecurity newssecurity news Pakistan
Reference: Qualys Security Blog — blog.qualys.com ↗