

vulnerability
Blog post
Waiting on a Node.js Upgrade? Build a Stopgap with the Controls You Own
Source: Qualys Security Blog · Published · Last checked 4 minutes ago · 1 min read
Publisher excerpt From Qualys Security Blog
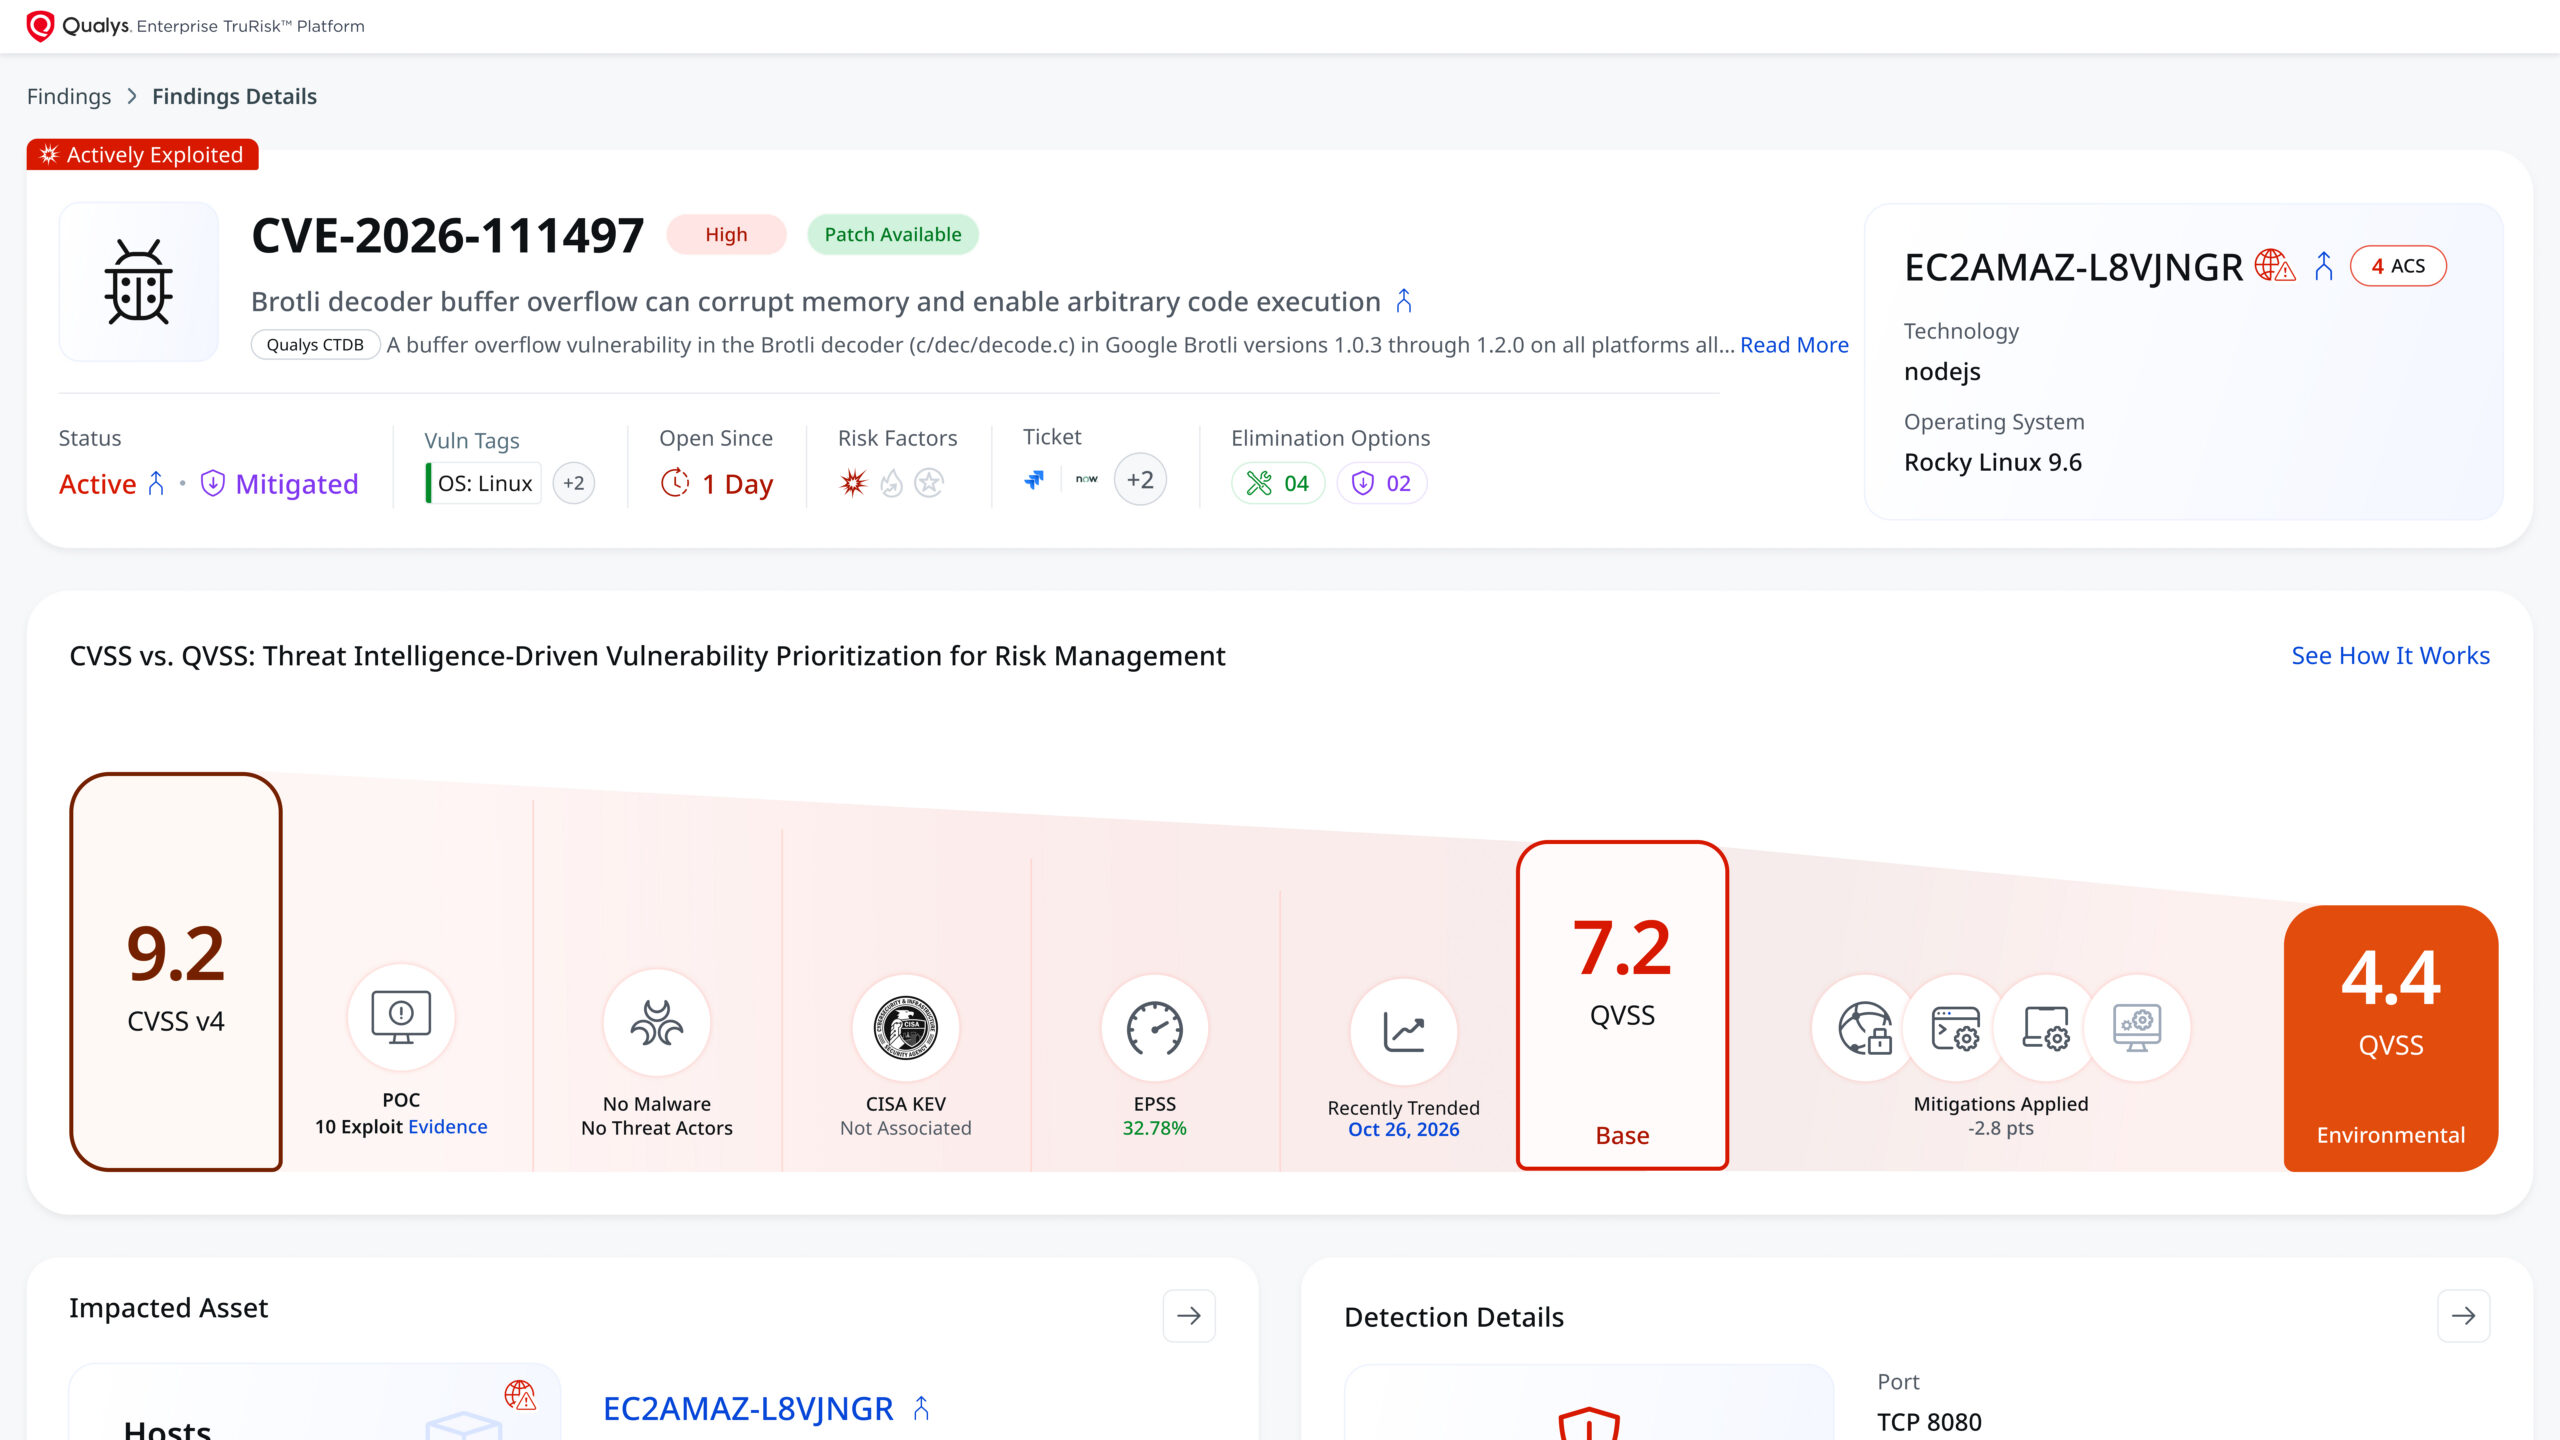
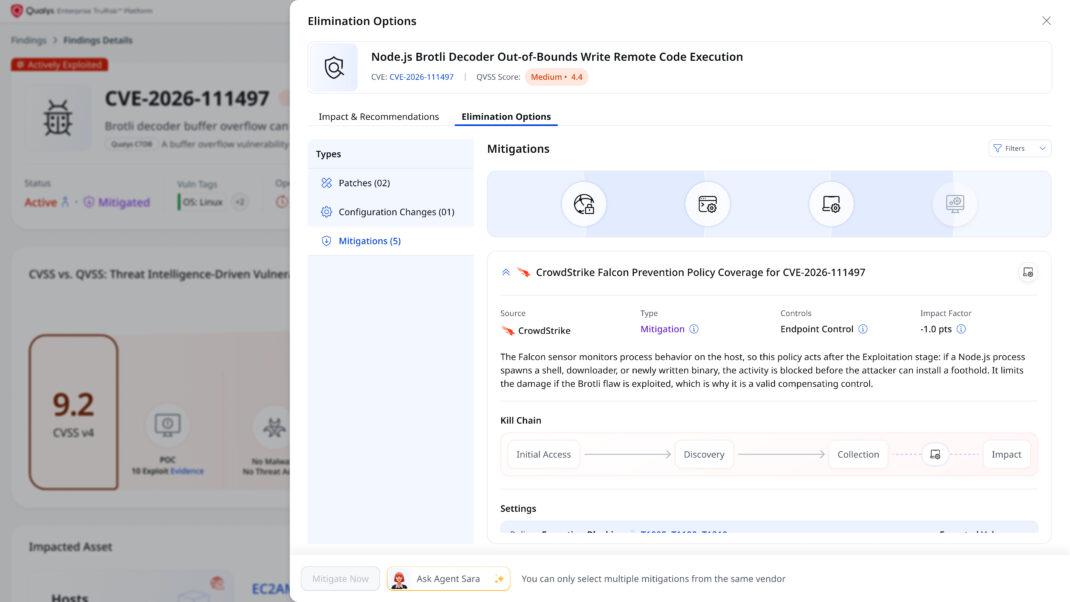
Executive Summary Node.js has fixed CVE-2026-111497, a Brotli decoder flaw that can permit remote code execution, in 22.23.4, 24.22.1, and 26.12.1, but upgrading at scale is slow. In Qualys telemetry, only 42,000 of roughly 3 million Node.js installations have been patched, and 1.7 million run end-of-life lines that will never receive a fix. In the […]
Excerpt only, shown with attribution. This content belongs to the original publisher and has not been independently verified by CyberSecurity.pk.
More images
Related CVEs
Keywords: remote code executionproduct and techcve-2026-111497nodejsqualys trurisksecurityupdatevulnerabilityvulnerability newsQualys Security Blogcybersecurity newssecurity news Pakistan
Reference: Qualys Security Blog — blog.qualys.com ↗