malware
Blog post
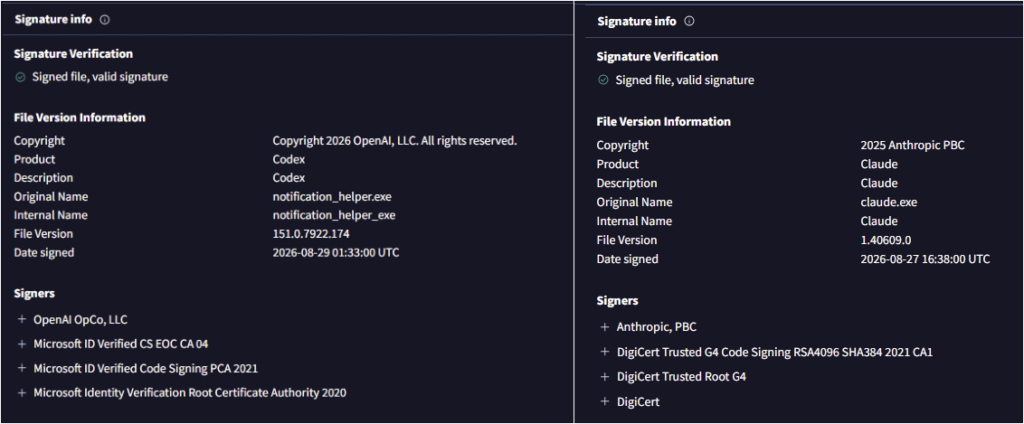
Tricks from the Past deployed via signed ChatGPT and Claude binaries
Source: Check Point Research · Published · Last checked 2 hours ago · 1 min read

Publisher excerpt From Check Point Research
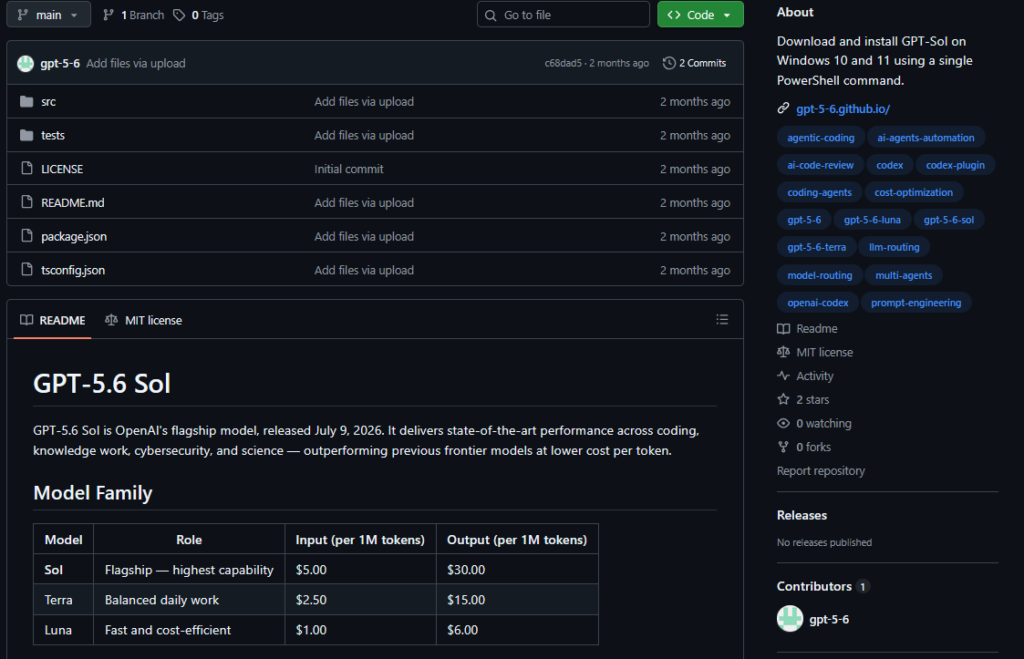
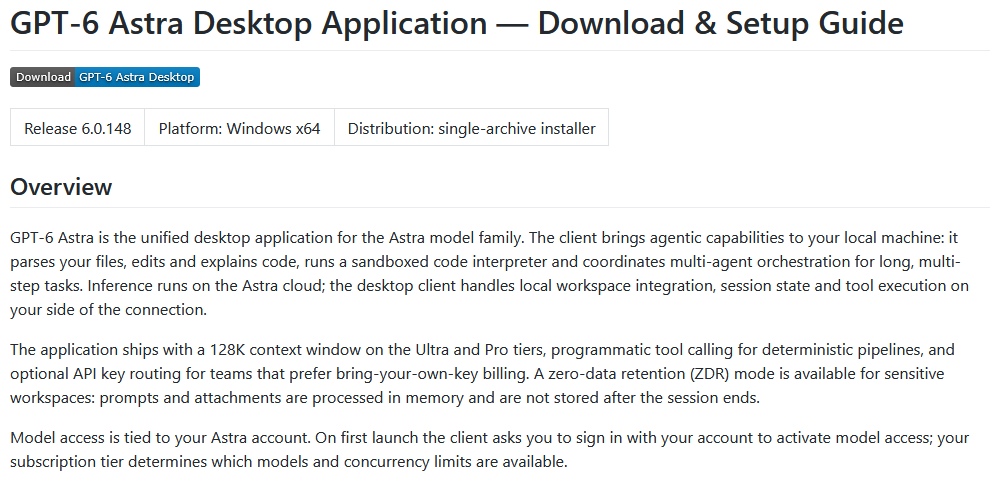
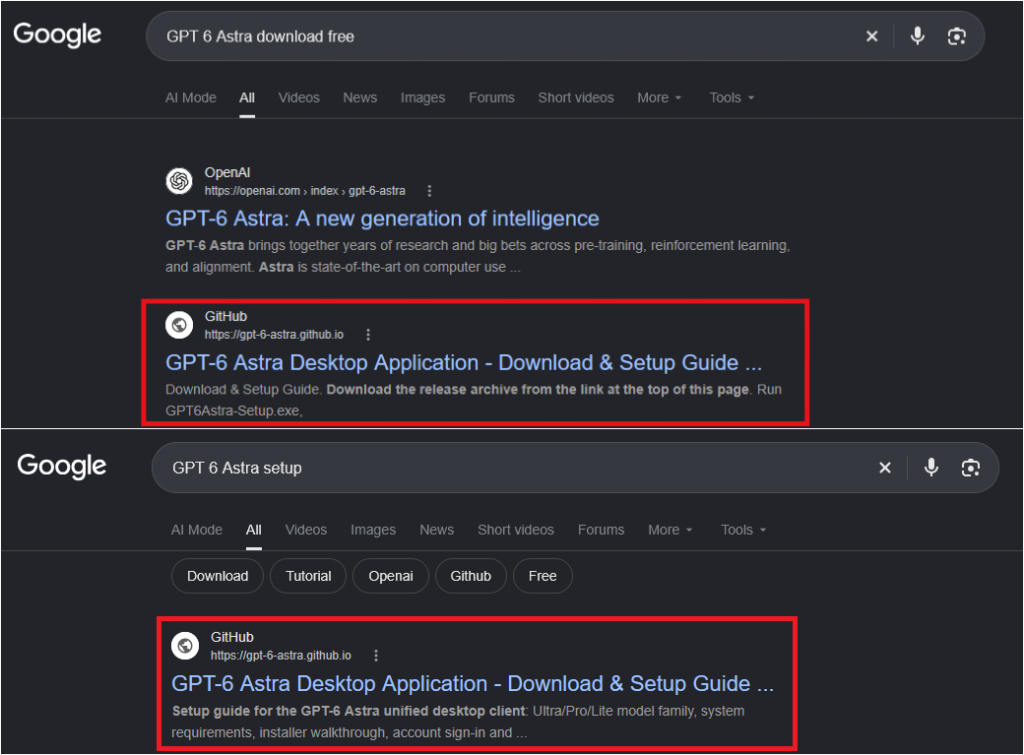
Key Points Introduction Over the past two months, we have been tracking a campaign that abuses the popularity of AI tools such as ChatGPT and Claude to spread a custom malware chain we call Yoba. The attackers use fake GitHub projects that pretend to be AI desktop applications like GPT-5.6 Sol, GPT-6 Astra, and Claude […] The post Tricks from the Past deployed via signed ChatGPT and Claude binaries appeared first on Check Point Research.
Excerpt only, shown with attribution. This content belongs to the original publisher and has not been independently verified by CyberSecurity.pk.
More images